Alice Averlong🏳️⚧️
foone@digipres.club
I've got two systems hooked up to my KVM and they have the same master password except with different capitalization.
I can HIGHLY recommend this if you want to feel like you're going slowly insane
 2
 1
 0
Andrew Zonenberg
azonenberg@ioc.exchange@foone I have two bank accounts that were supposed to use the same password except one of them limited user passwords to X characters and the password I chose was X+2 random alphanumeric characters. (silently truncated at registration time, that was fun to figure out)
So now bank A has an X character password and bank B has an X+2 character password where they share a common prefix. Guess how often I log into each one with the other's password...
1
0
0
Alice Averlong🏳️⚧️
foone@digipres.clubevil idea: a password system that has tempo restrictions
like it's "hunter2"
but you have to type "hunt" quickly" and "er2" at hunt-and-peck speeds, or it will reject.
5
0
0
ROTOPE~1 ⭐️
rotopenguin@mastodon.social@azonenberg @foone my login with my MVNO is 12 characters.
Their website's input box is limited to 10 characters.
1
0
0

Will Dormann
wdormann@infosec.exchange@rotopenguin @azonenberg @foone
Obviously client-side limitations are worthless. Time to find out if your login is 10 characters or 12. 😂
1
0
0
Andrew Zonenberg
azonenberg@ioc.exchange@wdormann @rotopenguin @foone lol that's what happened with my bank the reg form truncated but login didn't, or vice versa. Had to reset and shorten the password
1
0
0

David Chisnall (*Now with 50% more sarcasm!*)
david_chisnall@infosec.exchangeThere was a pen about 30 years ago that was intended for a very similar purpose. It turns out that humans are not that consistent about how their signatures look, but they do tend to be a lot more consistent about the sequence and ratios of pressures and directions of movement. Forgers would precisely recreate the shape but with a different sequence of movements, which would be easily flagged.
0
0
0

Audsbot
audsbot@fanglitch.space@foone this is not that but for a while i've been mulling over the idea of passwords that use non-printable characters, just to make things extra complicated and mess with keyloggers or people reading over your shoulder or what-have-you?
e.g. where the password looks like hunter2 but it's actually huer23[backspace][←][←][←]nt and someone inputting the apparent password without the extra inputs logs into a honeypot instead or something
1
0
0
Alice Averlong🏳️⚧️
foone@digipres.club@audsbot ugh, I've had that happen before on accident, where systems were not properly doing line editing.
so "hunterr<backspace>2" would not be accept as "hunter2"
0
0
0
Graham Sutherland / Polynomial
gsuberland@chaos.social@foone I remember writing a VB6 application to do this sort of thing back around 2002. iirc I started out with digraphs and trigraphs rather than syllables, for more of a "gait recognition" approach, then attempted to use WSAPI to extract phoneme groups but found that it didn't work how I wanted it to.
1
0
0
Graham Sutherland / Polynomial
gsuberland@chaos.social@foone although back then I didn't know what a digraph or trigraph was so I probably called it "groups" or something lol
0
0
0
phooky
phooky@hexa.club@foone telegraph key for passwords with a model that recognizes your "fist"
1
0
0
Trammell Hudson
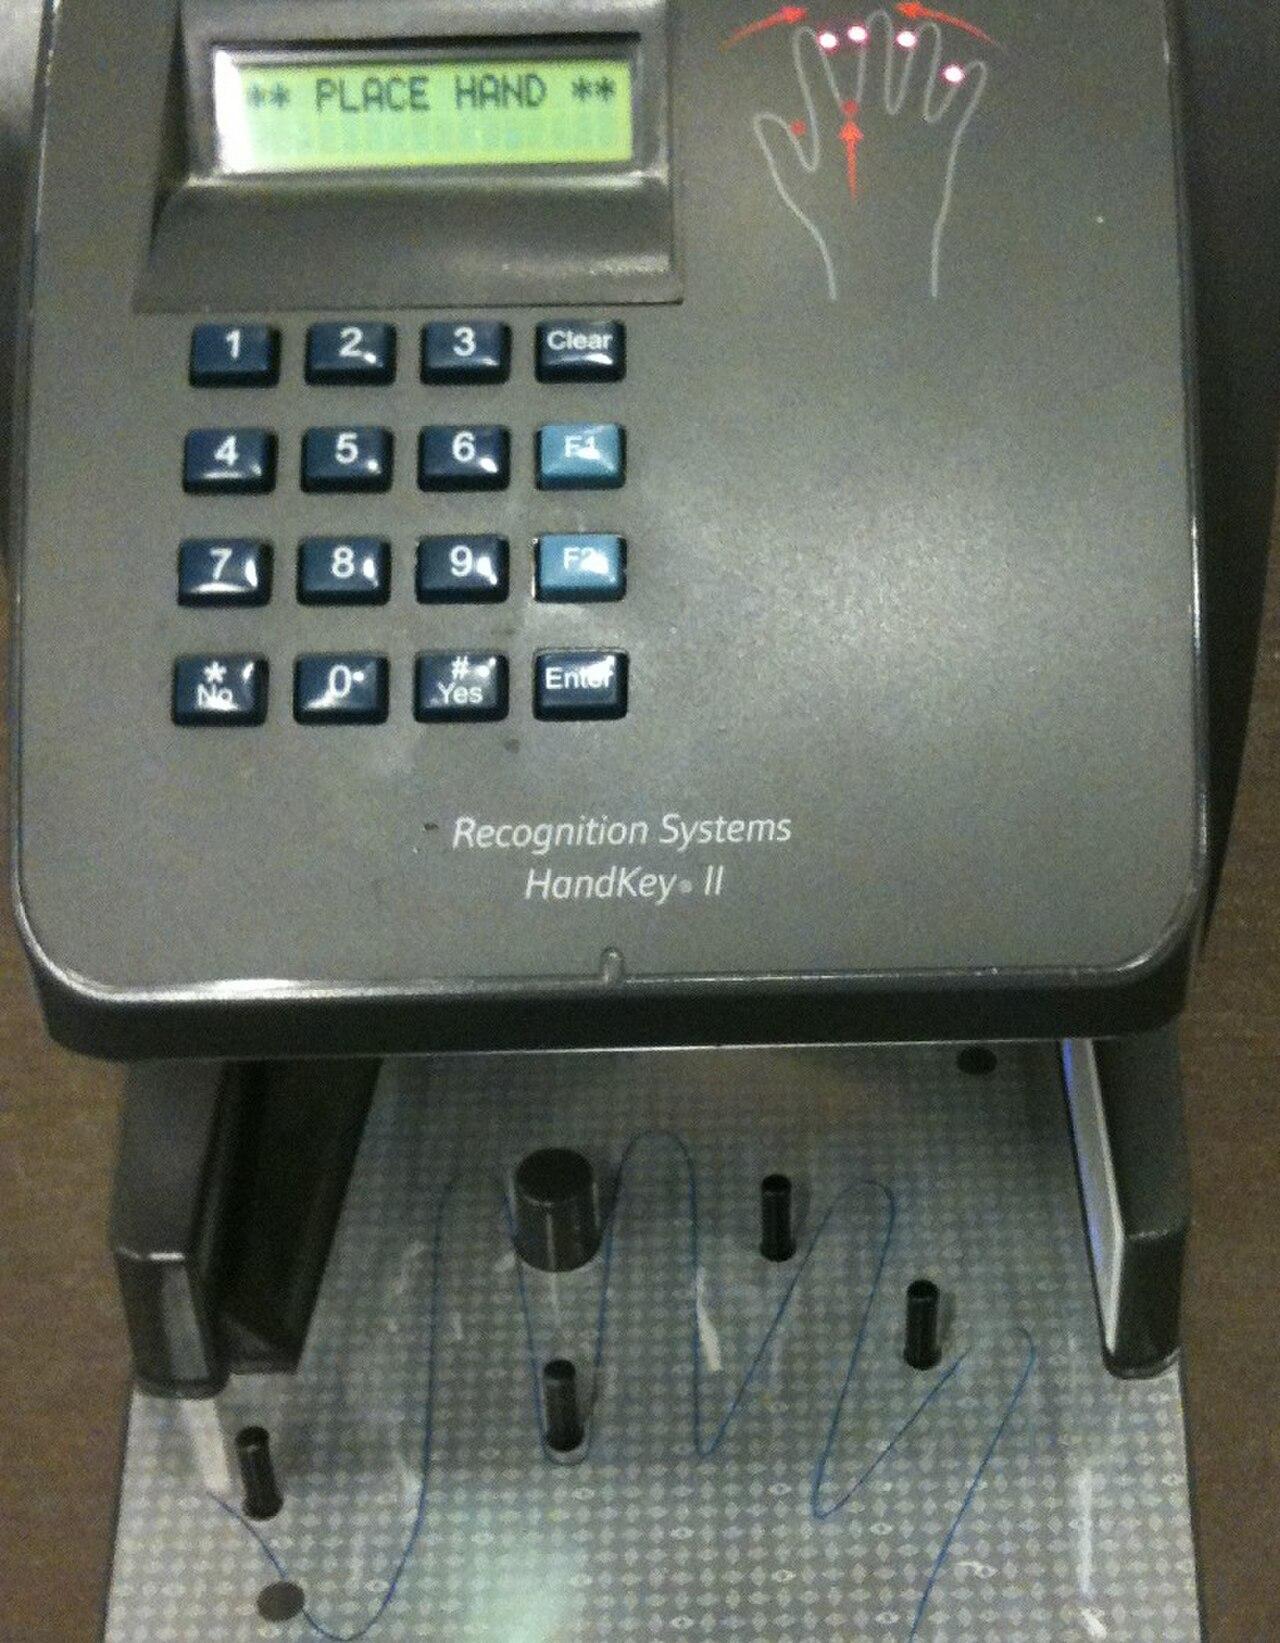
th@social.v.st@phooky @foone back in the 90s when I worked in Area Four we had this style hand geometry scanners that would recognize your literal fist https://en.wikipedia.org/wiki/Hand_geometry
 0
0
0
Cherri 🏳️⚧️
cherricock@mastodon.social@foone making my password "girlsex3765" to the tune of wonderwall
1
0
0
Alice Averlong🏳️⚧️
foone@digipres.club@cherricock very bold of you to assume that's not already my password
0
0
0

SnowFox
snowfox@tech.lgbt
@azonenberg @wdormann @rotopenguin @foone IIRC Yahoo's "secret question" answers stripped certain characters when setting them, but not when answering, and I had to manually figure out which "special characters" to exclude to get back into an account.
1
0
0
Geert Uytterhoeven
geert@society.oftrolls.com@snowfox @azonenberg @wdormann @rotopenguin @foone Netscape Navigator must have had an sprintf() in the password handling path, as I had to duplicate the percent sign when typing my password.
1
0
0

Geert Uytterhoeven
geert@society.oftrolls.com@ukleinek So probably you can crash (or worse) something using a carefully-crafted format string...
0
0
0