daniel:// stenberg://
bagder@mastodon.social
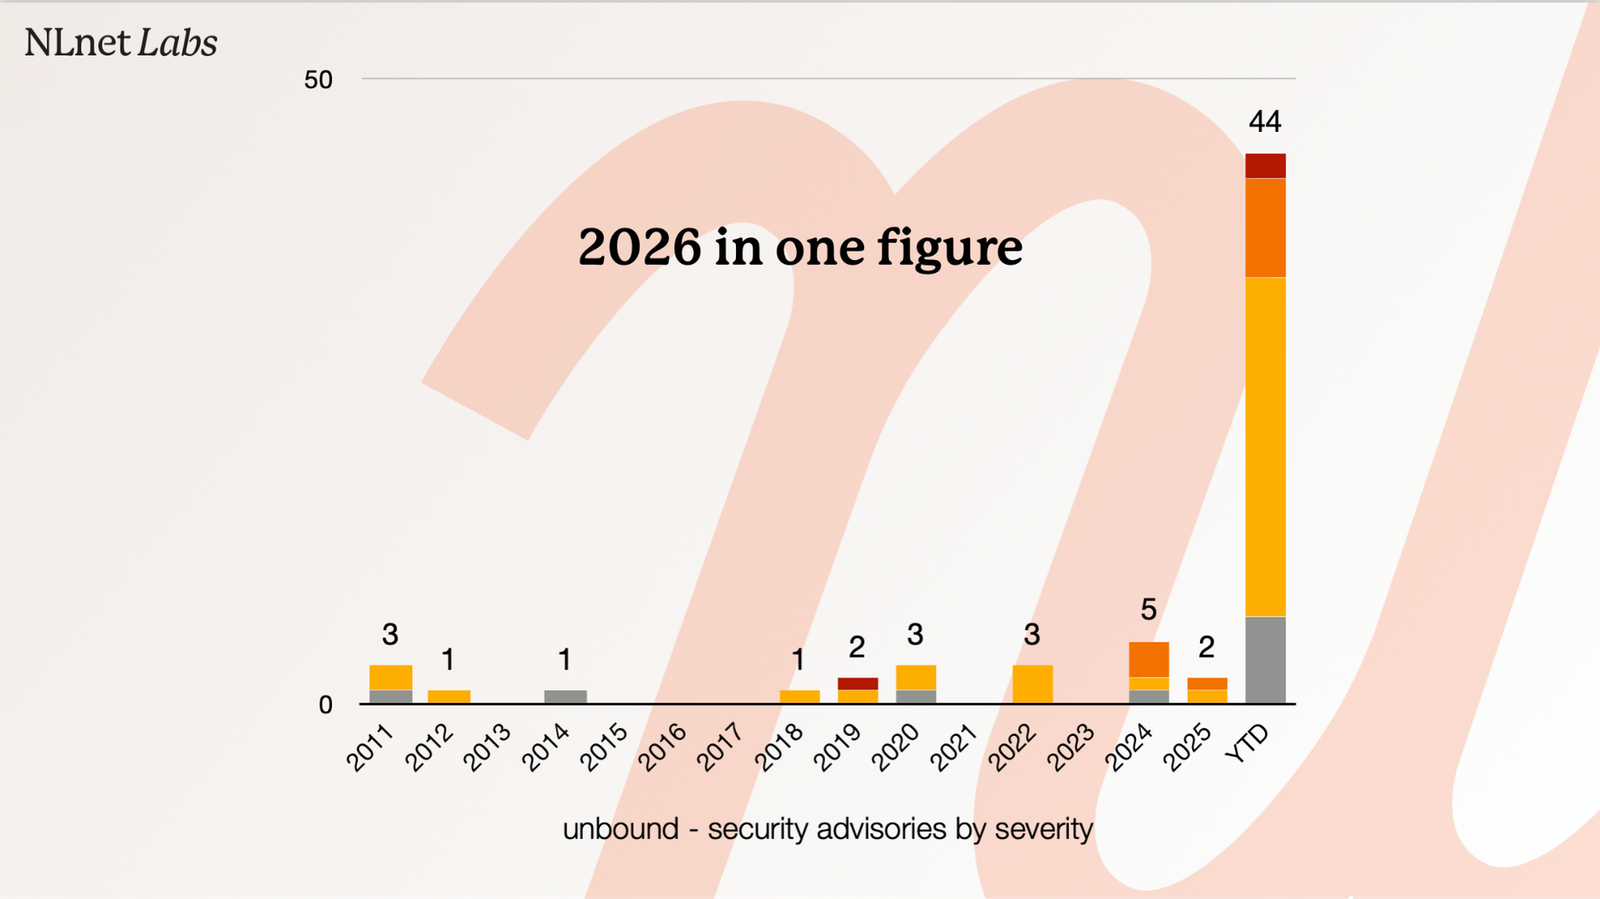
"for months on end now, most of our teams have just been triaging bugs and coordinating releases. It has truly taken all the fun out of the job"
https://blog.nlnetlabs.nl/maintaining-the-love-for-coding-in-the-time-of-ai/
 9
 13
 1

Guy Bockamp
guy_bockamp@mastodon.social@bagder was more fun, when all the bugs where left unnoticed?
1
0
0
daniel:// stenberg://
bagder@mastodon.social@guy_bockamp yes - but more importantly the reports came trickling in a few at a time
1
0
0

NLnet Labs
nlnetlabs@social.nlnetlabs.nl@bagder And as of right now, here's 9 more CVEs to add to this graph. https://github.com/NLnetLabs/unbound/releases/tag/release-1.26.1
1
0
0
daniel:// stenberg://
bagder@mastodon.social@nlnetlabs meanwhile, I sit here with at least 20 new curl CVEs in the queue to publish in sync with the next #curl release...
1
0
0
NLnet Labs
nlnetlabs@social.nlnetlabs.nl@bagder Good luck weathering the storm. Btw, is AISLE helping for you?
1
0
0
daniel:// stenberg://
bagder@mastodon.social@nlnetlabs they are. In finding flaws but also assessing and fixing.
0
0
0

Jim Fuller
jimfuller@mastodon.social@bagder hehe "This kind of contribution to your favorite open-source project may feel to you like “free as in beer” and “free as in speech” but to us it is like being handed a “free puppy”: well intended, but accepting it has big consequences for years to come." going to use 'free puppy' from now on excellant
0
0
0
Jules 🍺
julesbl@mastodon.me.uk
@bagder
That sounds like a total shit show, hopefully it all becomes too expensive for this sort of thing and then collapses
1
0
0
daniel:// stenberg://
bagder@mastodon.social@julesbl I don't think that's gonna happen. The LLMs have gone super cheap and you can do lots of this with open weights/running your own now. We can't reverse history.
1
1
0
Guy Bockamp
guy_bockamp@mastodon.social@bagder not as a deluge flooding everything to the brim, I suppose.
0
0
0
daniel:// stenberg://
bagder@mastodon.social@KittenKoder it seems odd to call them "slop" when they are accurate and fine though. But yes, no one finds vulnerabilities without AI anymore...
0
0
0
Krzysztof Kozlowski
krzk
0
0
2
Knut Branson
gooser3000@mastodon.social@bagder you don't think they'll run out of bugs to find soon?
0
0
0

Aad Schippers 🇪🇺
aadschippers@mastodon.social@bagder "As it stands, we see no other option than to publish the LLM policy that we have now, requiring all code and documentation contributions to be authored by a human." Seems like a wise decision to me.
Having read the blog and the replies to this post I feel that I have retired just in time. ;)
0
0
0

Jean-Baptiste Maillet
jbm@infosec.exchange@bagder could it be different if reported would NOT be credited for the report? 
(as in the "I have CVE on my resume" perverse incentive)
1
0
0
daniel:// stenberg://
bagder@mastodon.social@jbm maybe - but getting bugs reported is also good. We want to know about problems and fix them! Ignorance is not bliss in this regard.
0
0
0