
gudenau
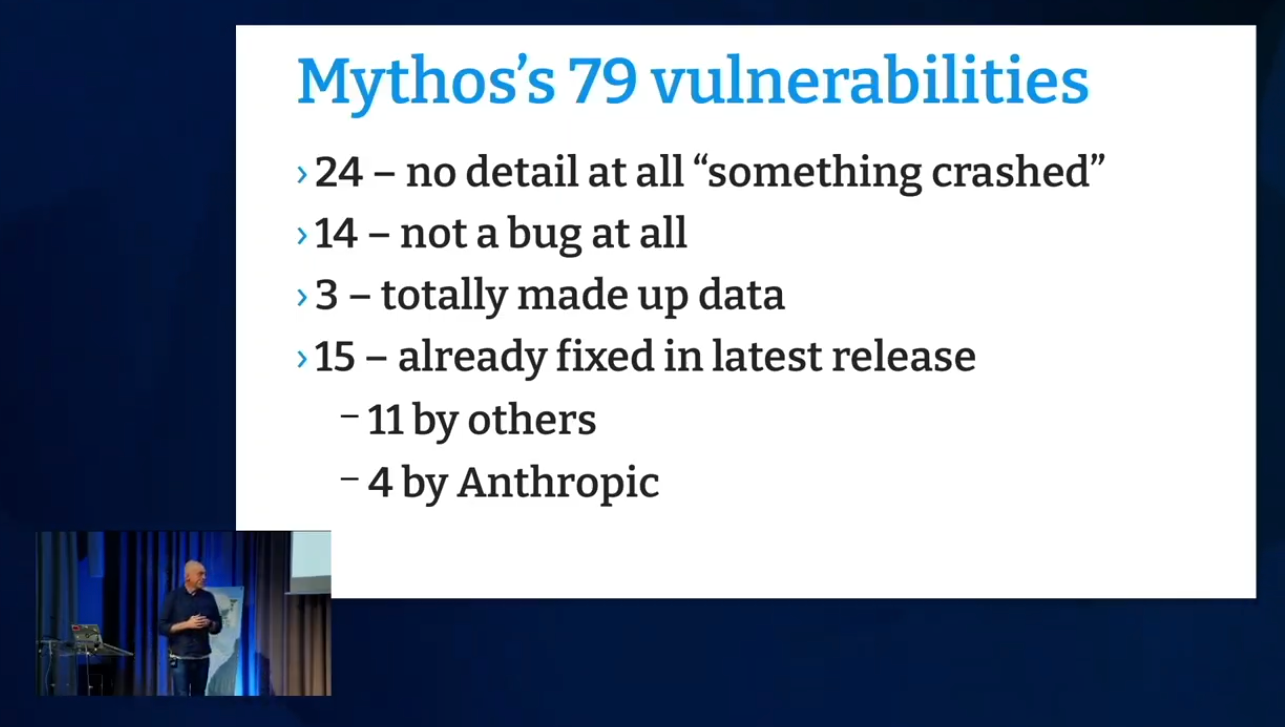
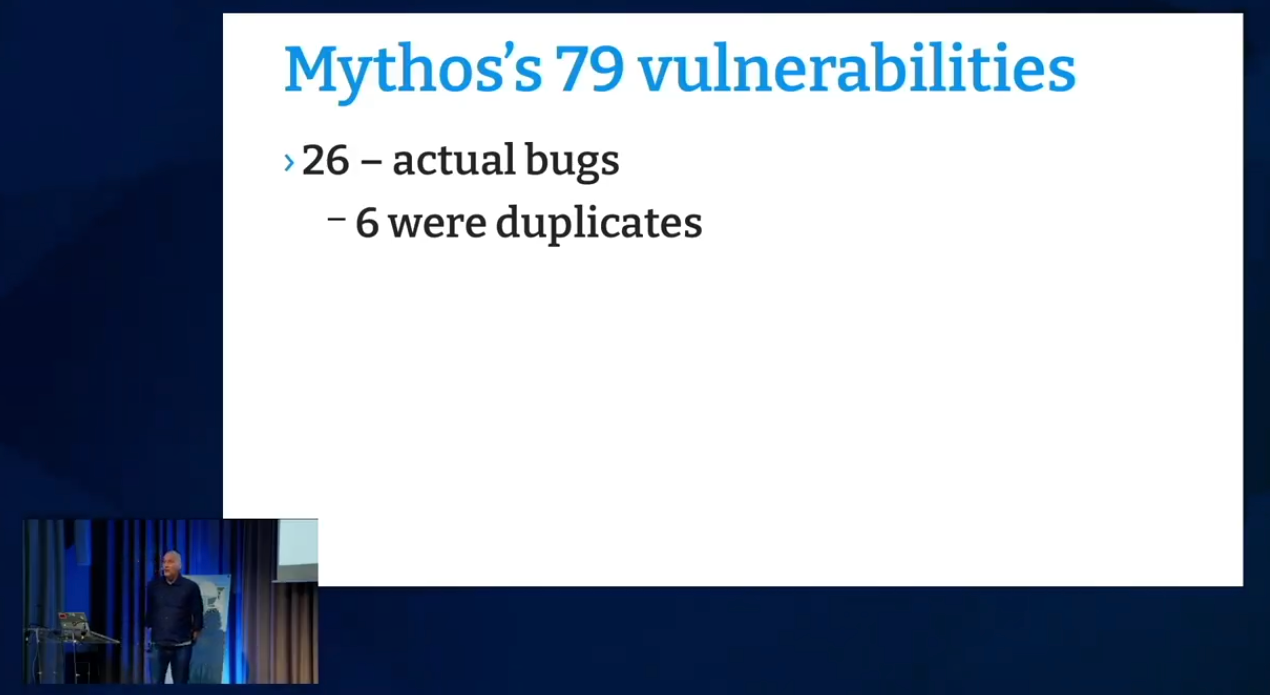
gudenau@hachyderm.io@KernelRecipes @gregkh I love how the LLM stans freak out every time something happens with them. But then every time receipts come without, it's not a big deal.
 0
 0
 0

Wanja
muvlon@hachyderm.io@KernelRecipes @gregkh Well, we're panicking anyway. Linux is approaching 2000 CVEs per release, and it doesn't matter much how many of those are found by AI. It's made any sensible approach to vulnerability management completely infeasible. And no, "always patch every server all at once immediately" is still not sensible. Everyone I'm talking to is either giving up entirely or actively looking at alternatives to Linux.
2
0
0
Greg K-H
gregkh
2
0
2
Wanja
muvlon@hachyderm.io@gregkh @KernelRecipes All software has security fixes, and a lot of it has CVEs, yes. But Linux has two orders of magnitude more CVEs than anything else we use. At some point, quantity becomes a quality all of its own. Specifically, the rate of CVEs puts an upper limit on the amount of human analysis that a given organization can invest into CVE triage. Once that dips below the amount of effort needed to even decide "do we run this code path at all?", you have little recourse but either patching everything unconditionally immediately (taking on a lot of operational risk) or blanket accepting security risks. For Linux, many organizations crossed that threshold last year.
And yes, Linux is a huge codebase, but that alone does not explain it. Chromium or Firefox are huge too.
1
0
1
Greg K-H
gregkhAlso bugs at our level are CVEs, while userspace programs don't have those same issues.
This is nothing new, other operating systems have the same issues and lists of CVEs. It's just that the corporate OSes don't actually publish all of their vulnerabilities because nothing requires them to, so they don't. Go blame them and the cve.org people, not us!
1
3
9
std::polar
sehe@fosstodon.org@muvlon @KernelRecipes @gregkh On the bright side, it prompts distributions to prune their kernels to a more sensible subset.
0
0
0
std::polar
sehe@fosstodon.org@gregkh @KernelRecipes @muvlon Differences are that Linux has historically been exempted from some scrutiny (because Open Source earned trust by default) and simultaneously Open Source makes it easier to identify areas where exploits could be found. It's akin to "the first-mover disadvantage" or "incumbent's disadvantage". Now that it becomes easier to poke at vulnerabilities, the transparency that gave a head-start comes back to bite, temporarily
0
0
0
plzupgrademe
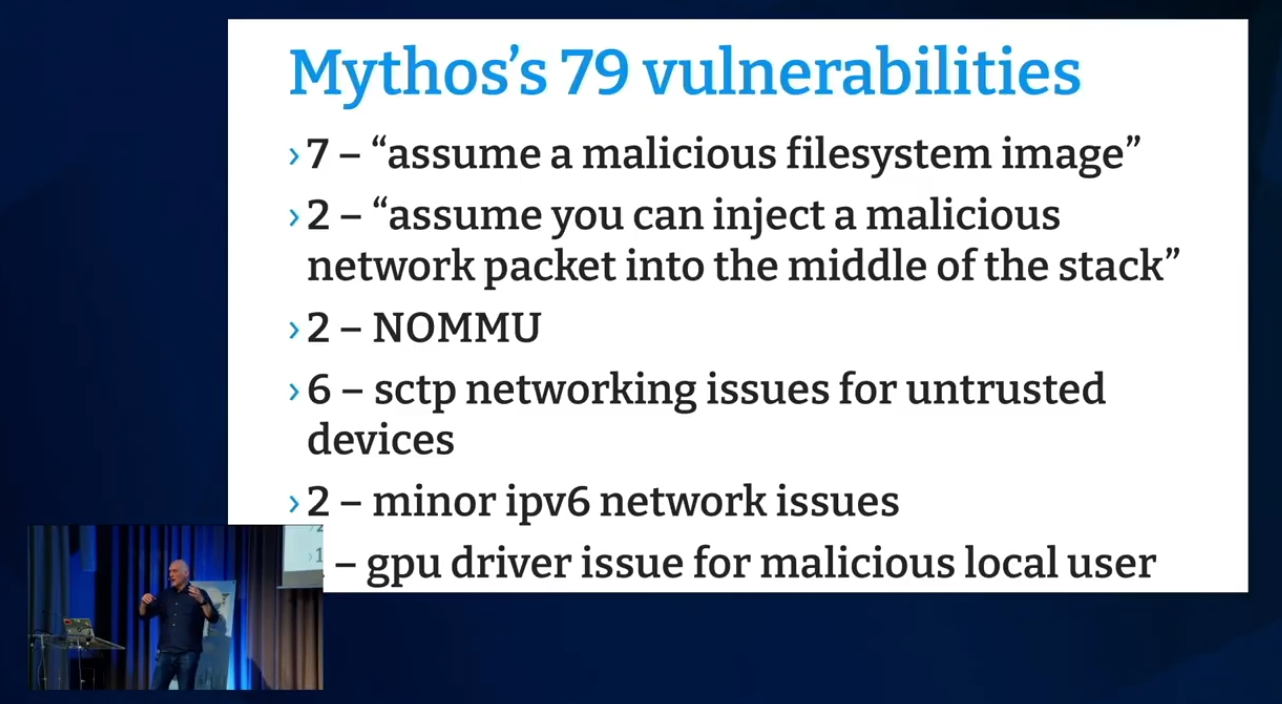
plzupgrademe@fedi.txw.ca@KernelRecipes @gregkh minor ipv6 network issues wasn’t on my bingo card today but nice
0
0
0
Philip Molloy
philipmolloy@mastodon.social@gregkh @KernelRecipes @muvlon we've partially addressed this confusion at ADI by generating CVE lists specific to our defconfigs:
https://analogdevicesinc.github.io/linux-security-vulns/#known-vulnerabilities
3
1
1
heine
heine@chaos.social@philipmolloy @gregkh @KernelRecipes @muvlon On what basis do you match a CVE to a certain defconfig? Is there tooling available or is this custom scripting?
1
0
0

Jean-Baptiste Maillet
jbm@infosec.exchange@philipmolloy @gregkh @KernelRecipes @muvlon this is great! Hello Qualcomm / Renesas / XYZ whatever / embedded distros (Buildroot, Yocto) I hope you're listening.
0
0
0
Greg K-H
gregkhThere's also many other older tools out there to get a simple "here are the files I am using for this kernel build" list, here's my very old version that has been used by Android in the past:
https://github.com/gregkh/gregkh-linux/blob/master/scripts/count_lines
1
1
3
Wanja
muvlon@hachyderm.io@gregkh @heine @KernelRecipes @philipmolloy I definitely have. Not on purpose, this is just my first time learning about it. This looks neat, thanks for the hint!
1
0
0
heine
heine@chaos.social@muvlon @gregkh @KernelRecipes @philipmolloy
Never heard of this before. To my defence, I see it’s not in 6.18 so it must be rather fresh 😅.
Should this work with a 6.18 kernel?
1
0
0
Greg K-H
gregkh
0
0
2