Posts
495Following
101Followers
5103
 repeated

Jed Brown
jedbrown@neuromatch.social
We all hate this
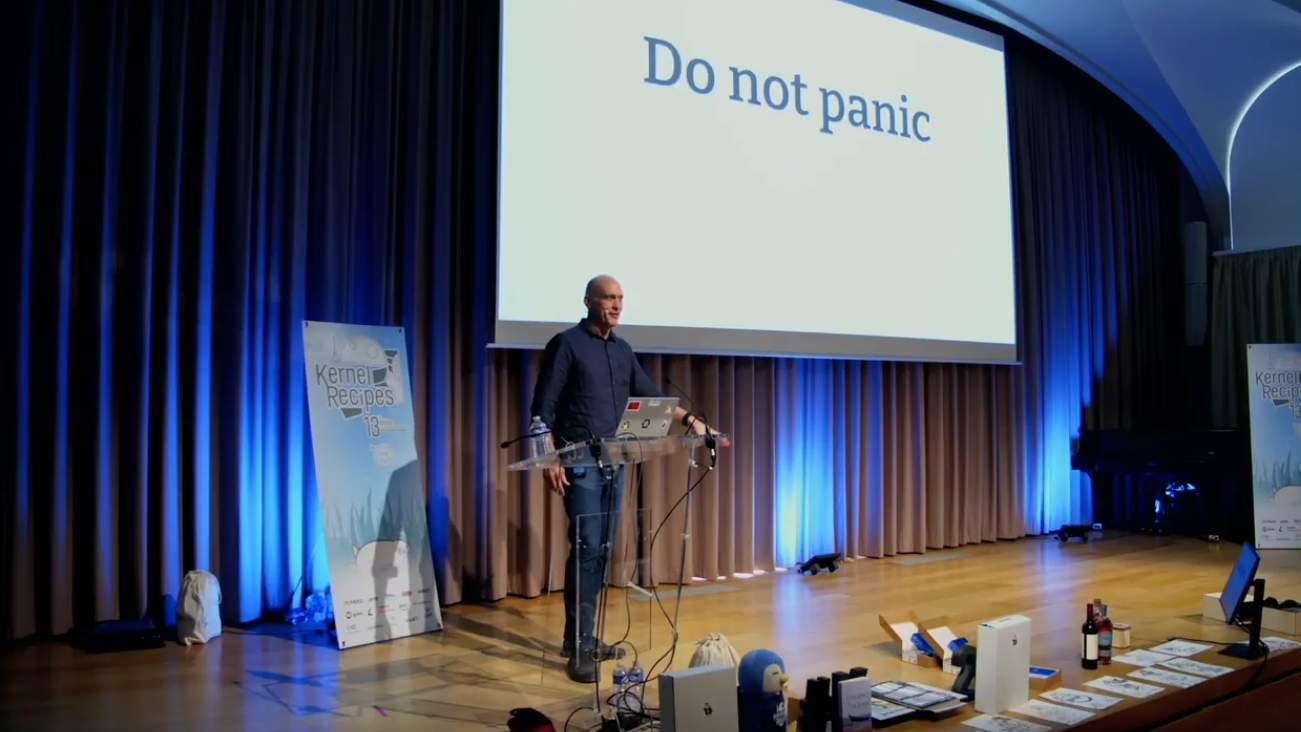
@gregkh dropping necessary bombs about LLMs in Linux security and development.
https://www.youtube.com/watch?v=NnV_cWeoo5Q
The purported 79 vulnerabilities were mostly bogus (not a bug, fabricated data) or had already been patched; the few real (all very minor) bugs took him an hour to fix. He says "do not panic", and emphasizes that time to apply patches is the main vulnerability these days (not an LLM problem).
"These are pattern-matching tools", "they do not have intent". (Vindicating to @emilymbender and @timnitGebru re "stochastic parrots"; it was accurate at the time and accurate today, protestations from boorish AI boosters notwithstanding.)
New code is 50% wrong, generated code is littered with new vulnerabilities; need to reject a lot but believes review processes are adequate to prevent a shipping a flood of LLM-generated vulnerabilities.
High false-positive rates make the models incredibly irritating. Cf. Coverity's post-mortem with a deterministic tool that had low false-positive rates.
Push back hard [on corporate marketing to developers]
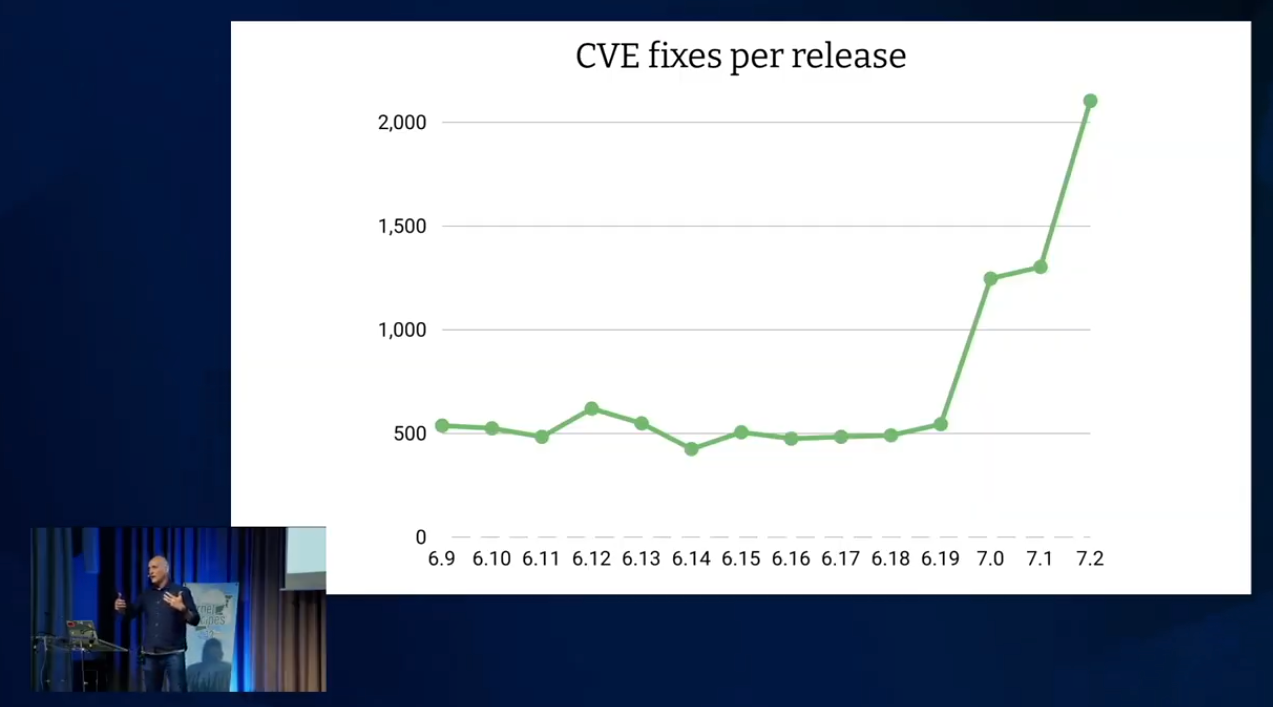
With regard to higher CVE rates:
We'll grind it down like we did with the fuzzers.
If you want to look for bugs with an LLM (which amounts to fuzzy pattern-matching), use a local model and never upload to platforms.
I have banned LLMs from driver staging, unless you have the hardware and can prove you have tested the patch. That's not what staging is for. Staging is to learn how to do development and get involved with our community. [...] Kernel development is all about trust. If I take patches from you and I don't know who you are, now I am responsible for that patch. [...] You need to build up trust.
It's put a lot of additional burden on us, as maintainers.
 1
7
 6
Greg K-H
gregkhAlso cve.org just crossed the 100000 numbering barrier just now, first time that ever has happened, hopefully no scripts broke. And yes, the kernel.org CNA has CVE-2026-100000 reserved, need to find a "good" bug for that one, suggestions welcome!
https://github.com/CVEProject/cvelistV5/tree/main/cves/2026/100xxx
 1
10
24
repeated

Thorsten Leemhuis (acct. 1/4)
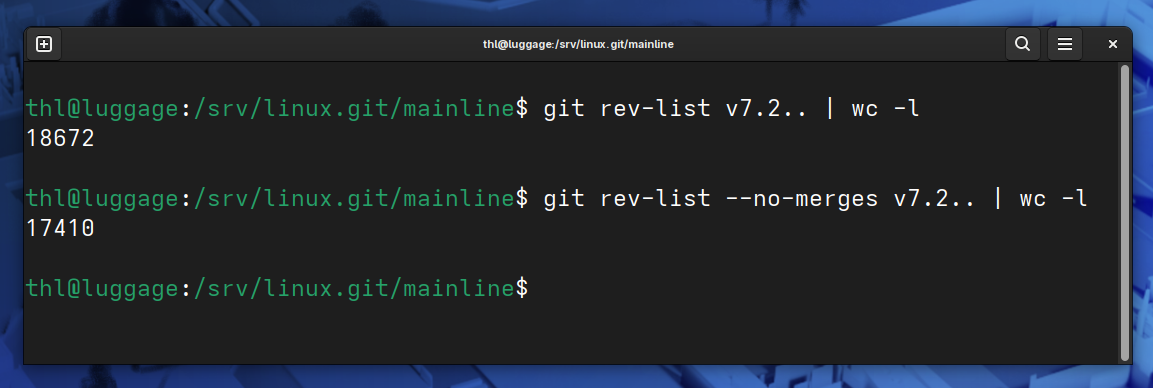
kernellogger@hachyderm.io#Linux 7.3, since a few hours ago, will definitely be the #kernel with the most commits, as right now it already has 18.672 (17.410 if you ignore merges).
The previous record holder was 6.7, which had 18.404 (17.284) -- and was bigger than other releases at that time because it contained nearly 3,000 commits of bcachefs history.
For more stats on #LinuxKernel releases, see https://docs.google.com/spreadsheets/d/1_yH7lFmZxAoSWrtsd8tGu3befG4zIcMnytB1ml4pQQM/edit?usp=sharing
 0
2
0
repeated
K. Ryabitsev-Prime 🍁
monsieuricon
https://slides.com/mricon/maintainer-container
Also attached as PDF.
 0
7
17
Greg K-H
gregkh 2
27
103
repeated
Kernel Recipes
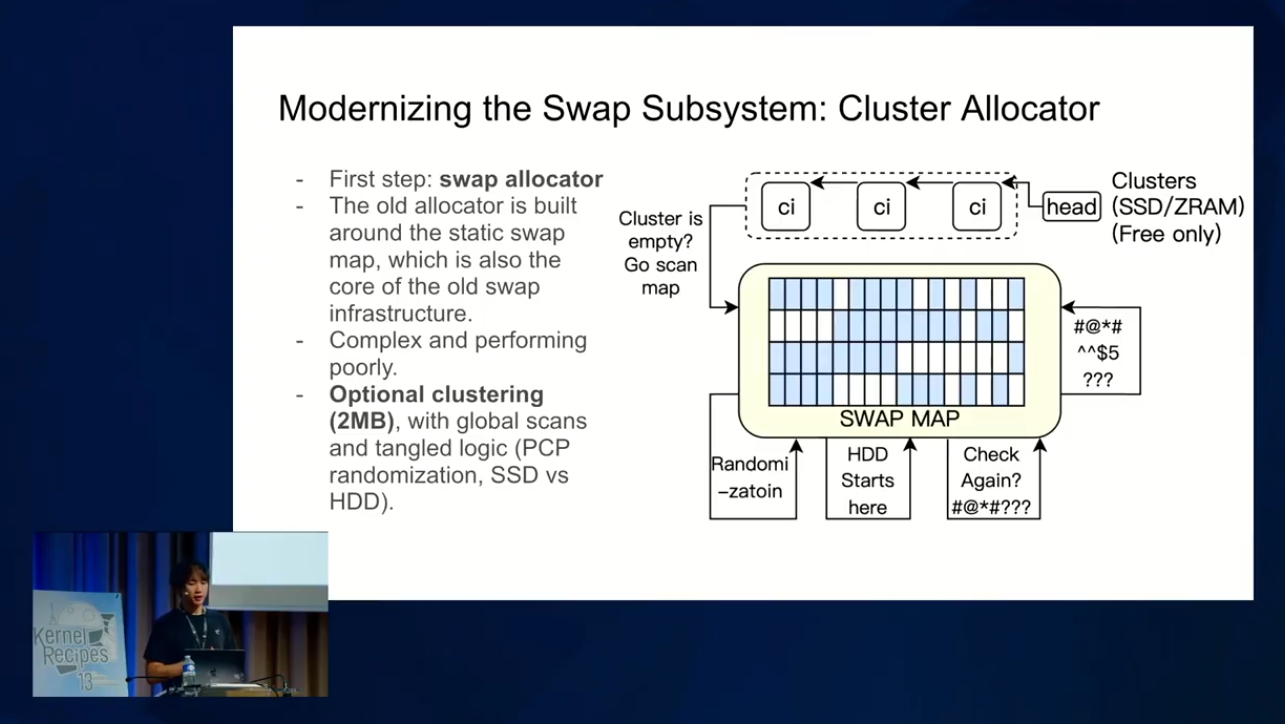
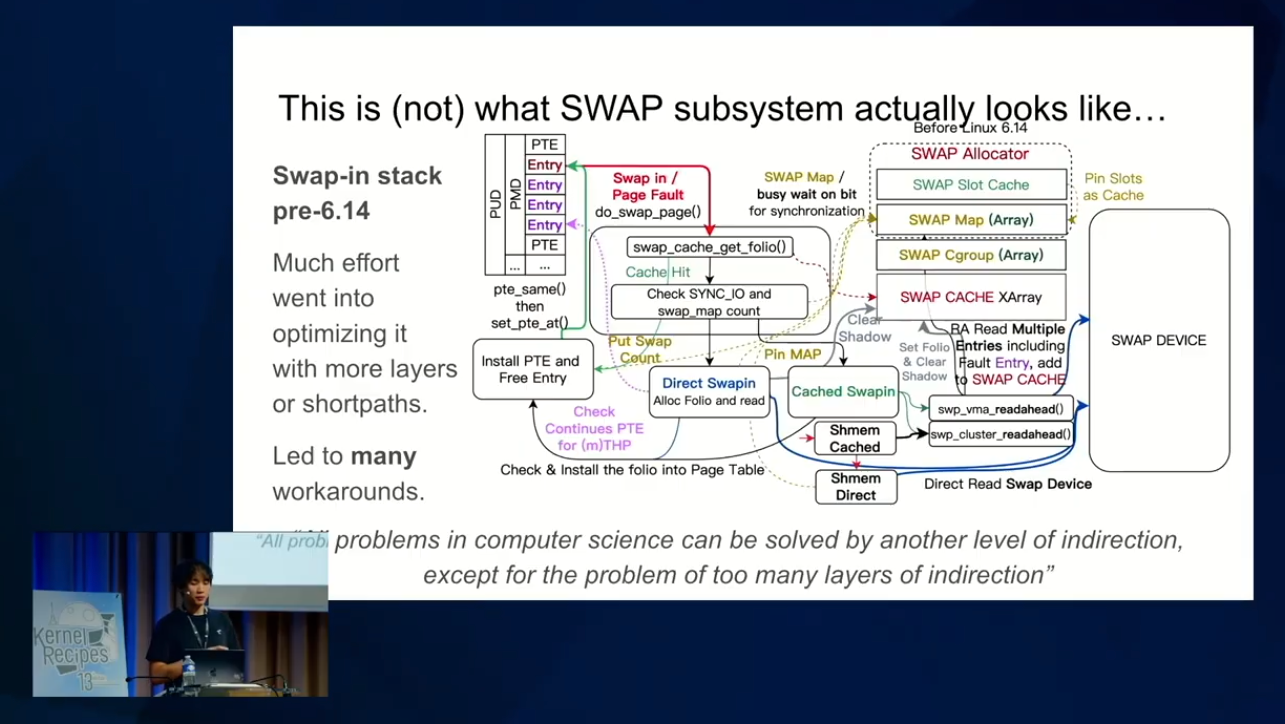
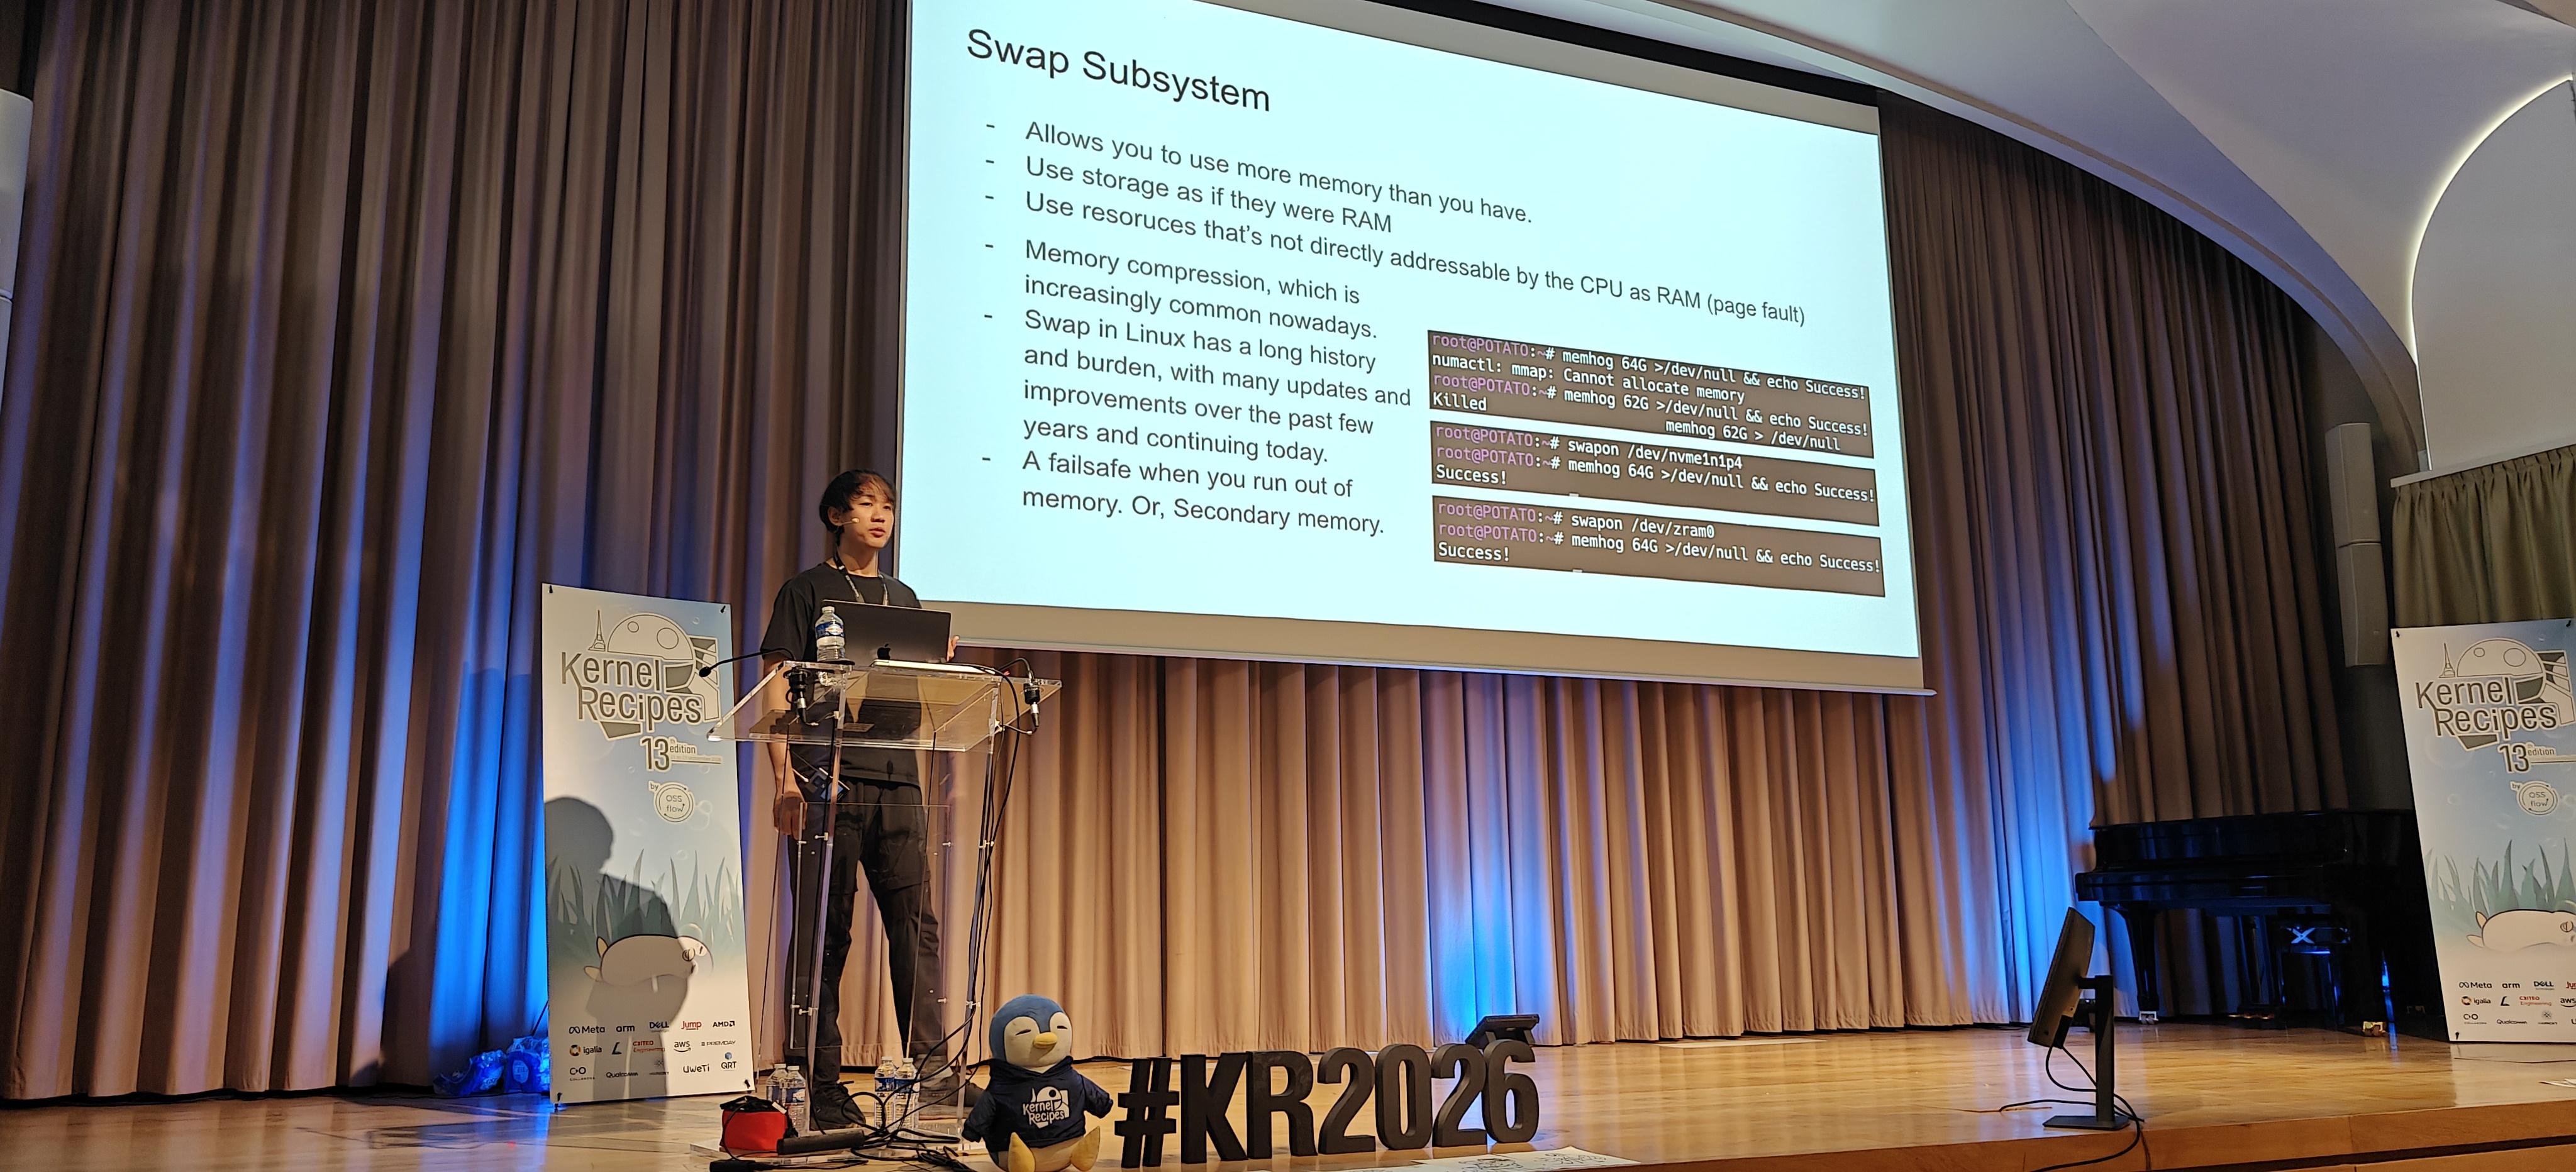
KernelRecipes@fosstodon.orgKairui Song is starting the last day of the conference : Swap and Memory Reclaim: Squeezing Out More RAM
What was SWAP subsystem before and now: Too many indirections kill indirections
 0
1
0
repeated
Kernel Recipes
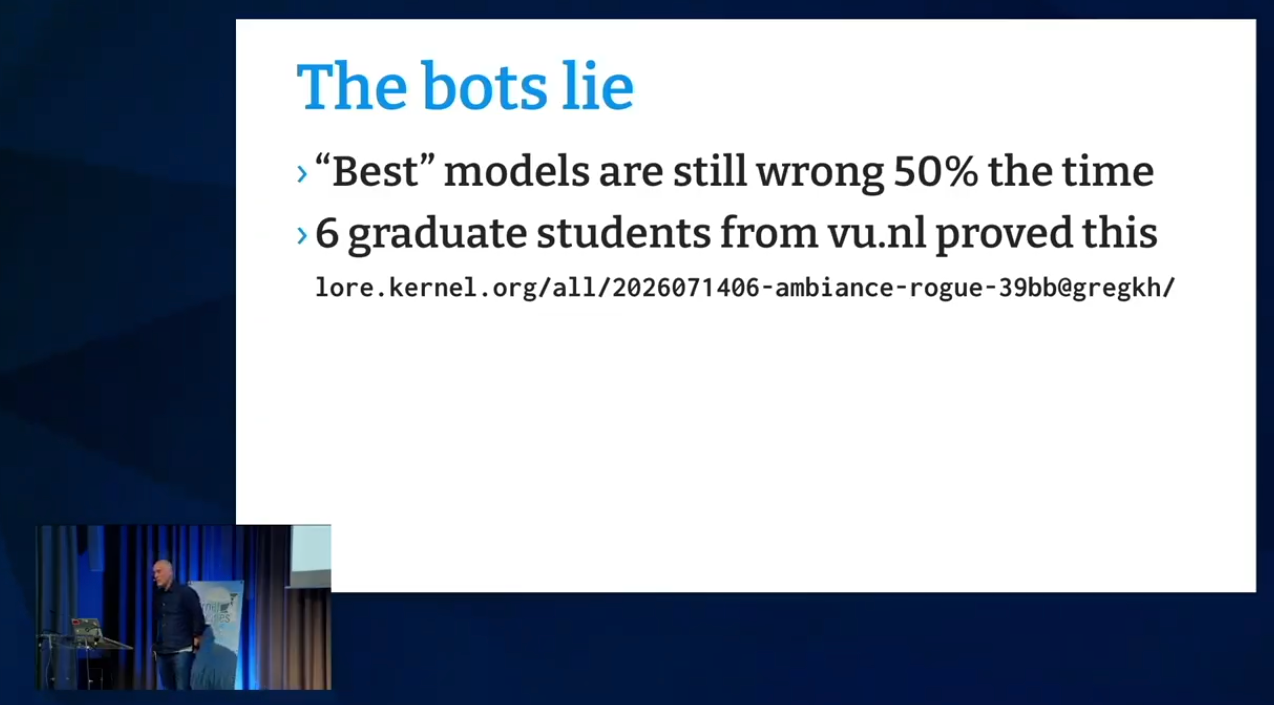
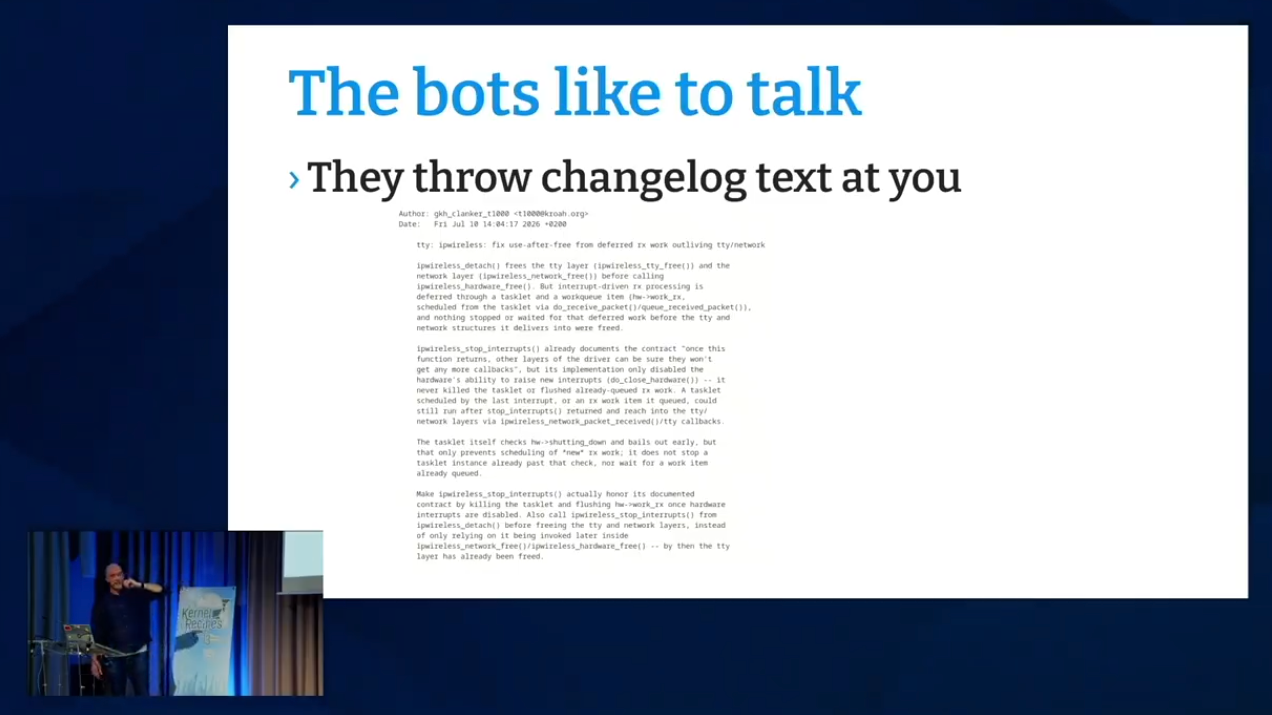
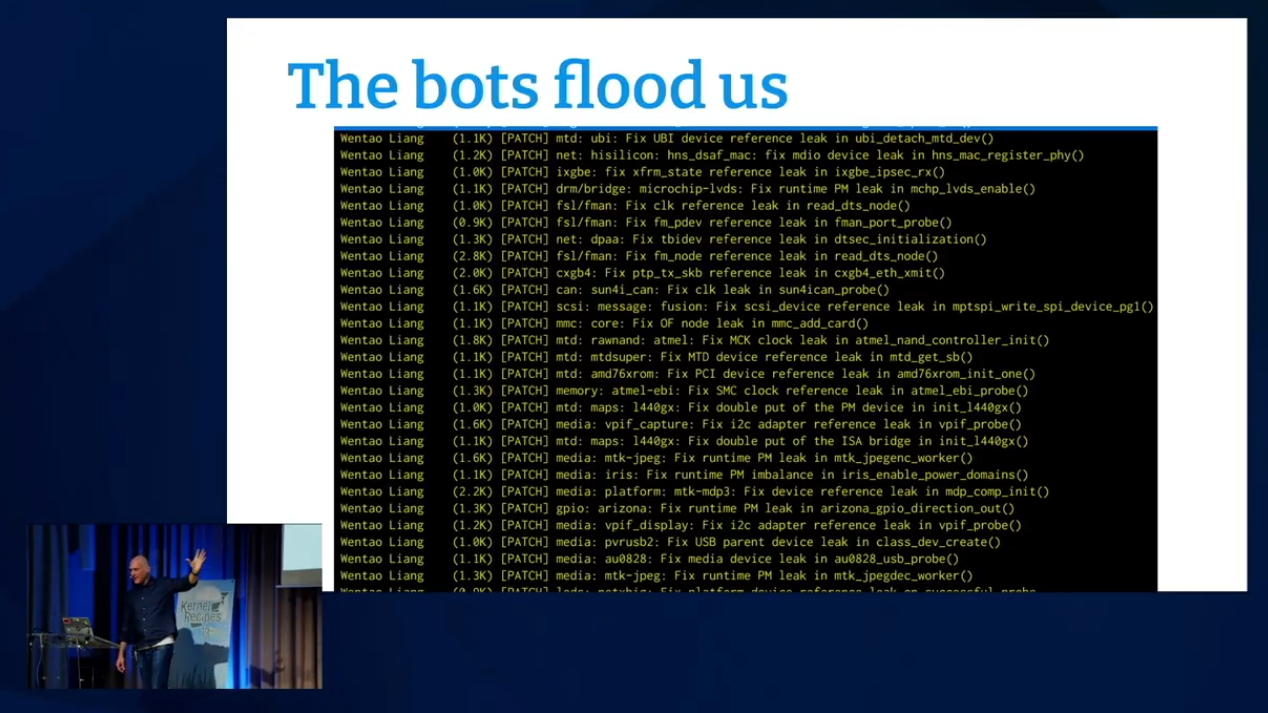
KernelRecipes@fosstodon.orgWhat kernel maintainers think of bots, in four slides:
they talk: endless changelogs nobody asked for
they flood: dozens of "fix leak" patches before your first coffee
they lie: the "best" models are still wrong half the time
they leak: whatever you tell them, they'll tell someone else
So basically... the perfect coworker!
#kr2026
 2
7
0
repeated
Kernel Recipes
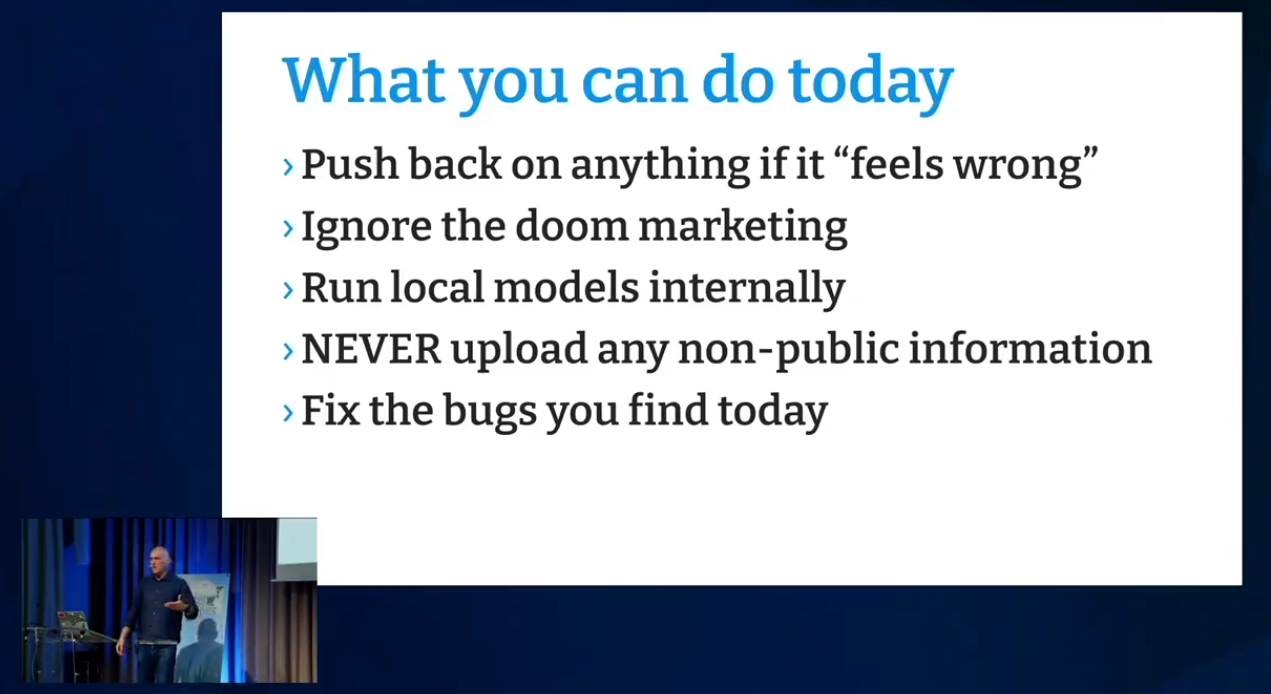
KernelRecipes@fosstodon.orgSurvival guide for the age of bots, #kr2026 edition:
If it feels wrong, it probably is
Ignore the doom marketing
Keep your models at home
NEVER feed them anything non-public
Found a bug? Fix it. Today. Yourself.
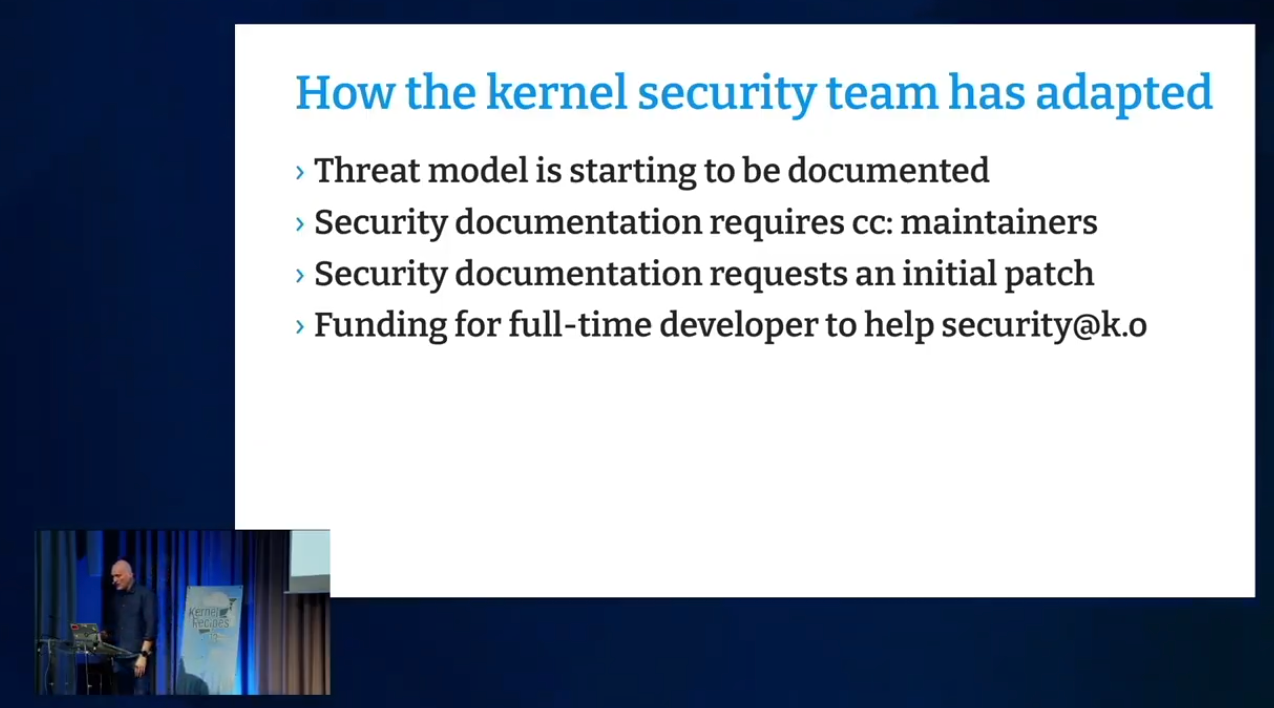
Meanwhile, the kernel security team now asks for a patch with your report. Revolutionary concept.
 0
2
0
repeated
 repeated
tante
tante@tldr.nettime.org"Executives working on AI at Microsoft and OpenAI admitted what its critics have been saying all along: Large language models are predatory pieces of technology that have been built on what a Microsoft executive called “an astonishing theft of unprecedented proportions,” and the “largest theft of labor in human history.” An internal Microsoft document said generative AI products have created a “doom loop” that is killing “the entire web.”"
(Article title: ‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft)
2
7
1
repeated
daniel:// stenberg://
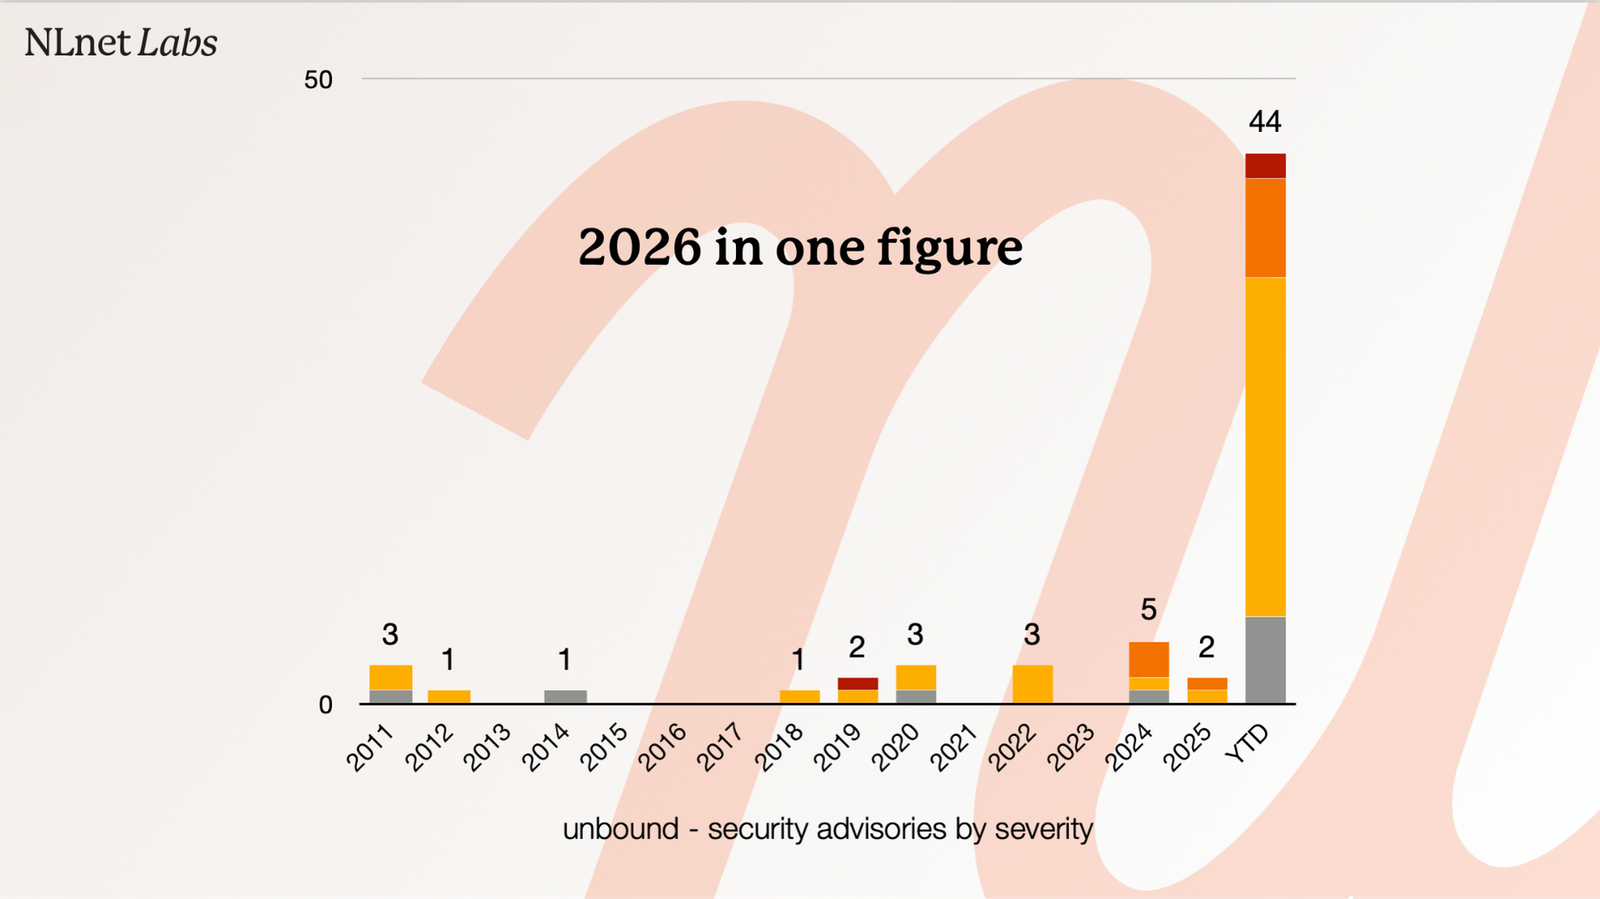
bagder@mastodon.social"for months on end now, most of our teams have just been triaging bugs and coordinating releases. It has truly taken all the fun out of the job"
https://blog.nlnetlabs.nl/maintaining-the-love-for-coding-in-the-time-of-ai/
 9
13
1
repeated
Thorsten Leemhuis (acct. 1/4)
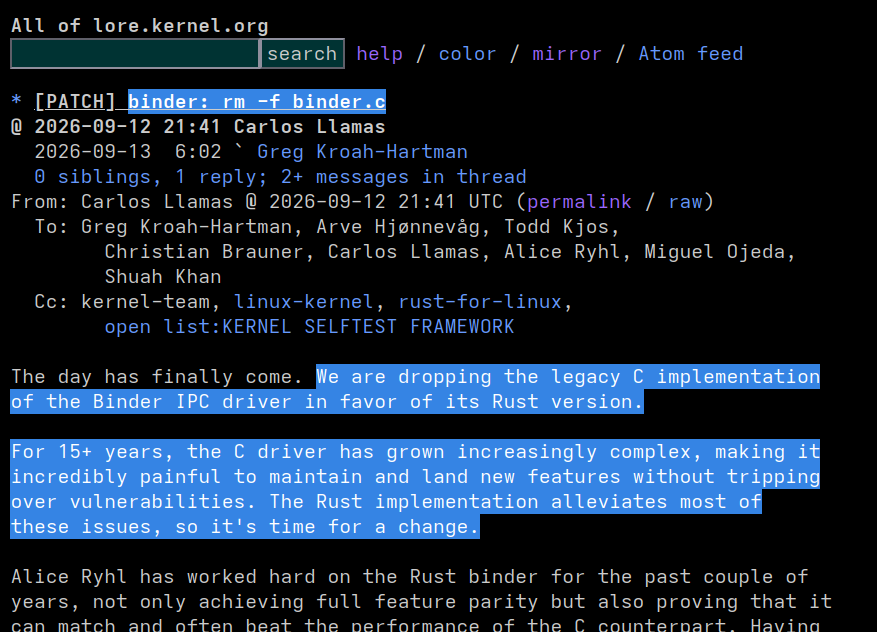
kernellogger@hachyderm.ioLooks like the legacy C implementation of the #Binder IPC driver will soon be removed from #Linux in favor of its #Rust version:
https://lore.kernel.org/all/rm-c-binder@google.com/
""Long live the new Rust Binder king!""
#Rustlang #LinuxKernel #Kernel
 4
8
0
Greg K-H
gregkhThis might be a “record” for stable kernel -rc releases. Not really a record I want to ever beat…
     version  queued
	5.10:	 798
	5.15:	 935
	6.1:	1191
	6.6:	1424
	6.12:	1376
	6.18:	1518
	7.2:	1815
	total:	9057
OpenSSF
openssf@social.lfx.devThe September 11 CRA reporting milestone is here.
Our new community guide explains manufacturers’ reporting obligations and how open source maintainers and stewards can prepare for collaboration when vulnerabilities affect downstream products.
 0
1
0
repeated
daniel:// stenberg://
bagder@mastodon.socialOpen Call for Nominations: European Open Source Awards 2027
Please consider taking a minute and tell us who we should recognize and honor this time around! We need to know about the heroes to be able to celebrate them.
https://awards.europeanopensource.academy/nomination-process
1
7
0

Greg K-H
gregkhhttps://digital-strategy.ec.europa.eu/en/library/cyber-resilience-act-implementation-frequently-asked-questions
So while many of us were ready to start the reporting process, it is good that we have a bit more time for the tools and infrastructure to get solid before we have to start using it.
2
7
21
repeated
Thorsten Leemhuis (acct. 1/4)
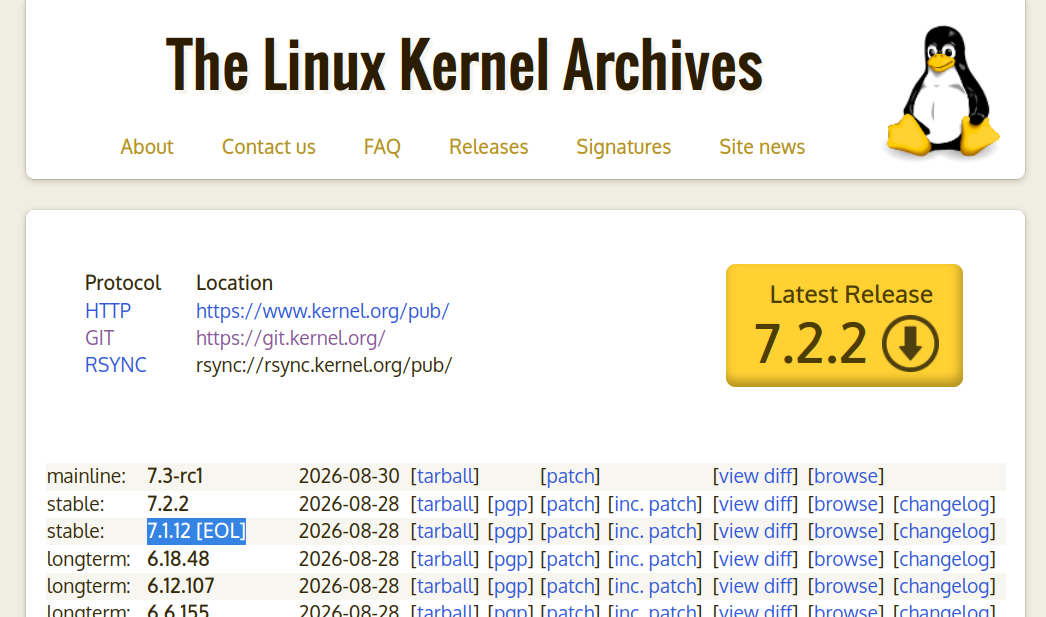
kernellogger@hachyderm.io#Linux 7.1 is now unsupported upstream – @gregkh just announced that while releasing 7.1.13 and a bunch of other new stable and longterm #kernel releases:
""Note, the 7.1.y kernel series is now end-of-life. Please move to the 7.2.y kernel series at this point in time.""
https://lore.kernel.org/all/2026090223-botanical-purging-2933@gregkh/
 0
2
1
repeated
bluca
bluca@fosstodon.org#systemd v262~rc1 is out! If you don't help testing it out, YOUR favourite third party service will be next on the takeover list
https://github.com/systemd/systemd/releases#release-v262-rc1
1
5
0
repeated