Posts
203Following
432Followers
346
 repeated

Matt Keeter
mjk@hachyderm.io
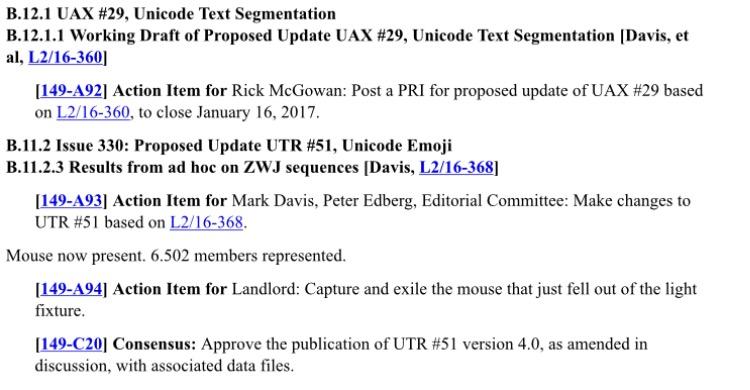
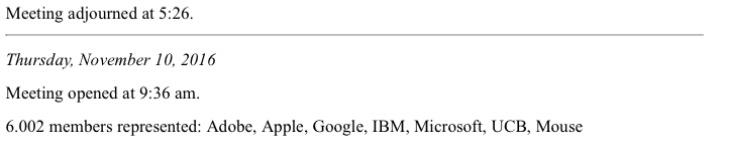
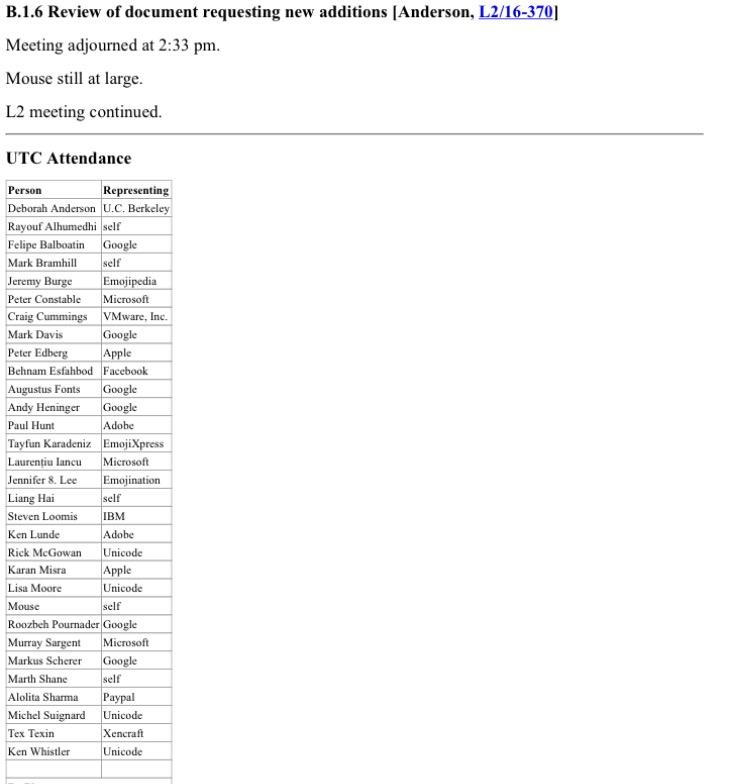
happy 10-year anniversary of the Unicode Mouse Incident, for those who celebrate!
the mouse fell out of a light fixture, was listed as an official meeting attendee, and given 0.002 votes
 3
31
 2
repeated
themadhatter
themadhatter@mastodon.social"A # prompt indicates the attacker has obtained root. Disconnect from the network, then from society."
Via @GossiTheDog
0
2
0
repeated
Anna Liberty
liberty@mathstodon.xyzPerhaps counterintuitively, I believe now is the best time to embrace and share personal and communal creativity.
Folks are drowning in slop. Everywhere you look there is content generated by "Generative AI". People are tired of it.
So start a blog. Write some code. Create art. Don't use "AI". Make it clear that you reject it so others can find and promote you. Promote others who do the same.
The world is drowning in noise and desperate for signal. Share that signal.
1
7
0
repeated
kookie 🏳️⚧️🏴☠️
kookie@chaosfem.twSo I boosted a slopped cartoon about chess pieces cuddling. Turns out that account is just a constant stream of slop and one of them just happened to go a bit viral.
The OG artist of the chess carton makes a lot more wholesome and cute comics.
It makes me angry that the slop version is getting spread so far and wide while the originals aren't.
Go take a break from your day and enjoy these: https://www.wawawiwacomics.com/comics
4
8
0
repeated
Kit Bashir
Unixbigot@aus.socialFor those struggling with democracy, here's how we do it (not perfectly but I think pretty fairly) in Australia.
1. Everyone is expected to vote. There is a small fine if you don't show up and get checked off the electoral roll. If you choose to vote by scribbling a dick and balls on your ballot paper, whatever. Campaigning is focused on issues not on "please go vote". Getting a call, text or email from a political party is pretty rare.
2. There is a government department tasked with making it easy and feasible for everyone to vote. Waiting longer than 5 mins is very rare. There is generally a polling place within walking distance. Pre-poll and postal voting are available for those who can't make it on the day (which is always a Saturday).
3. Voting is by ranked-choice. You cannot "waste" your vote, if your first preference comes last, your vote transfers to your second preferenace (and so on). This means independents and smaller parties get elected and can have influence.
4. After the election, parties receive a small amount of funding for each first-preference vote they receive. This means putting the Lazycrats *second* after the FreeKittensParty hurts the Lazycrats in their hip pocket, even if the FKP could never win.
5. Voting places are friendly. Usually they are a school or church where an impromptu jumble sale and barbecue happens. I have never seen a cop, soldier or even a display of anger at a polling place.
6. Campaign workers must stay a certain distance away from the polling place. Advertising must end the day before the election.
7. Election campaigns last about 4 weeks, not years.
You don't have to make this so fucking hard.
3
12
0
repeated
Kim van Wyk
kimvanwyk@fosstodon.org
@GrahamDowns au contraire, while git via CLI is permitted and vastly preferred over button clicking in an editor, the best way to use it is with Magit: https://magit.vc/
This has the minor requirement of knowing how to use Emacs, but that's surely already a skill everyone has.
0
2
1
repeated
tante
tante@tldr.nettime.org"In a world where all of our compute is in massive distant opaque datacenters, where a tiny cartel of gigantic tech companies control nearly the whole supply chain, one of the few things that you still can have agency over is your own server on the Internet."
(Article title: Why You Should Care About The Political Project of Twisted)
0
3
0
repeated
Damien Miller
damienmiller@hachyderm.ioOpenSSH 10.6p2 has been released with a workaround for a critical vulnerability.
https://openssh.com/releasenotes.html#10.6p2
If you operate a Linux system that uses musl libc without PAM (Alpine Linux is one example) then stop reading and set PasswordAuthentication=no or disable SSH for these systems IMMEDIATELY.
This vulnerability does not exist on non-Linux systems, Linux/glibc systems and Linux systems that use PAM for password authentication.
We consider the root cause of this bug to be outside OpenSSH itself, but we're in a good position to deliver a mitigation quickly.
We are making this release as fast as possible (we learned of the problem yesterday) because we have recently observed multiple cases of rapid bug rediscovery by AI agents, sometimes within hours, and so now consider long embargo periods to be a dangerous practice that primarily benefits attackers.
Thanks for Özgün Kültekin of Wakefield (wakefield.co) for reporting this problem to us and for the Alpine Linux developers for making an updated release available at very short notice.
5
30
1
repeated
Pozorvlak
pozorvlak@mathstodon.xyzRE: https://infosec.exchange/@david_chisnall/117540788341445069
I can't remember who I learned this from (maybe @raganwald?) but a good trick for reading computer science papers if you work in industry is
1. Find a bunch of papers on the problem you need to solve.
2. Notice what baseline they're all comparing their new shiny techniques to.
3. Implement that instead.
Update: it was Jay Kreps, probably via Avery Pennarun's blog: https://x.com/jaykreps/status/219977241839411200?a=W6GRXkYLlAZ3X-AlM_Y&s=19 Thanks to @DRMacIver for tracking it down.
3
7
0
repeated
Multipath TCP
mptcpOkay, maybe that's caused by an advertisement from Anthropic and linked to CVE-2026-98432? 🤔
BTW, MPTCP was one exploitation path for this issue in TCP, there could be others. So upgrade your server (and/or block IPv4 options), don't "just" disable MPTCP.
(Not sure how such a high score got assigned for something hard to reproduce in practice and probably impossible on the internet where IPv4 options are often blocked. But that's good to remind people to keep their system up to date 🙂)
And thank you Eric for the fix!
#MPTCP
1
37
44
repeated
 repeated
 repeated

Human Ghostwriter 
HG@beige.party
I work for and with rich people because they pay me lots to rent my brain. I have learned some things:
1. "Rich" is normally some combination of time, talent, luck, and fear. Luck is always one of the components. Rarely do my clients credit luck.
2. It does not take much money (relative) to become insulated from most consequences of daily life. That insulation rapidly severs people from people who work for a living.
3. People who inherit their wealth are contemptible. So are a lot of people who have worked for their money, but trust fund babies (who I am in the business of creating) have a strong tendency to be entitled, imperious, incompetent shits.
4. I'm really smart and really good at what I do. This is absolutely not a prerequisite for becoming rich and can even be counter-productive. Many of the people I work with are not particularly smart or talented, and that doesn't matter if you find a good racket and can sock away the money.
5. Back to people who inherit their money: as someone who will inherit basically a steak dinner and a heightened risk of Alzheimer's, I know nobody is coming to save me. I save as much as I can understanding that it may be a fool's errand. I resent people who have the luxury of knowing they cannot die from poverty because one day a mountain of dough is going to fall on them.
6. The estate tax should apply to as many people as possible and it should be confiscatory. Without it, we end up with these neo-feudalist enclaves of the corpulent rich, the grandchildren of ruthless/fortunate/gifted men, check-cashers who live off exploitation alone.
7. We do not need rich people.
Sorry, I'm in a mood. Endrant.
1
6
0
repeated

David Chisnall (*Now with 50% more sarcasm!*)
david_chisnall@infosec.exchangeReminder to people who have international meetings: the next week is George W Bush Golfing Time. The USA and Europe had an agreement to move clocks at the same time, so the time difference remained constant. George W Bush decided he wanted a few weeks more golfing time, so unilaterally moved the USA’s Daylight Saving Time. This move remains in effect so there are a few weeks of annoying disruption each year.
I made the mistake of flying the first time this happened, which is how I knew about it: the airlines were unprepared and sold me tickets on two flights where the time change meant that my slightly tight 45-minute change turned into a -15 minute connection time (fortunately the second flight was on a route they flew every two hours so I was only an hour late)l
0
1
0
repeated
Aral Balkan
aral@mastodon.ar.alHey, @EUCommission, fuck you too.
***
On Wednesday, EU Member States approved a change to the GDPR that would put the profit-making interests of OpenAI, Anthropic, Google, Meta and SpaceX over European's fundamental right to data protection. According to the approved text, processing personal data “in the context of AI” should automatically be lawful. In particular, Big Tech would be able to use all personal data collected over the past decades with virtually no restrictions, as long as this happens “in the context” of AI. Schrems: “Under the agreed text, the profits of AI companies would typically trump European’s fundamental right to privacy. This is nothing but a digital expropriation of Europeans.”
https://noyb.eu/en/ai-eu-member-states-approve-digital-expropriation-europeans-ai-companies
#privacy #humanRights #EU #BigTech #corporatocracy #fascism
5
18
1
repeated

Christine Lemmer-Webber
cwebber@social.coopAn article on Aftermath about how depressing AI slop has made emulation and decompilation projects, and crushed existing communities https://aftermath.site/ai-slop-hobbies-in-software-emulation/
And hey, it links to me and @glyph's blogposts
(Thx for the heads up @mostol)
2
6
0
repeated
 repeated

Paul Chaignon
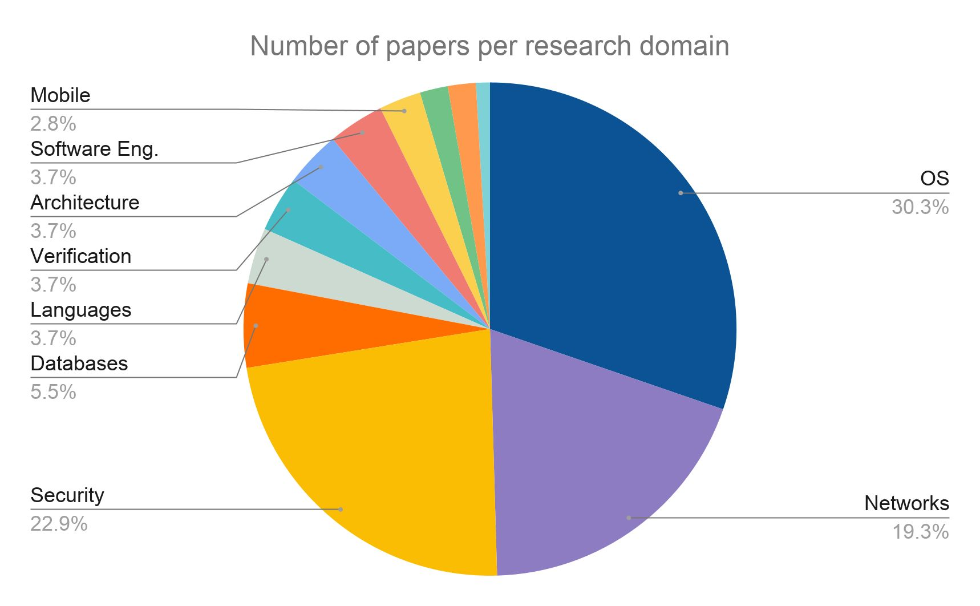
pchaigno@hachyderm.ioI've uploaded the slides for my talk at #LinuxPlumbers on eBPF research: https://pchaigno.github.io/assets/Linux%20Plumbers%202026%20eBPF%20Research.pdf.
I discussed the methodology to build the list of BPF papers at https://pchaigno.github.io/bpf/2025/01/07/research-papers-bpf.html. I then used it to plot some statistics and navigate the different topics and questions being investigated in academia. I'll try to follow up with blog posts for more details.
Video: https://www.youtube.com/live/UQCglEwWwT4?si=idejC6sU2DiTadDi&t=991
 0
3
0
repeated
Flüpke
fluepke@chaos.socialThe private key (D) is 4.
No joke.
Verification:
openssl pkey -in key.pem -pubout -outform DER | openssl dgst -sha256
openssl x509 -in cert.pem -pubkey -noout | openssl pkey -pubin -outform DER | openssl dgst -sha256
4
10
0
repeated

Quentin Monnet
qeole@hachyderm.ioReading from ring buffer maps, multi-split BTF support, new program signature scheme: bpftool v7.8 comes with some new features, and a number of bug fixes.
https://github.com/libbpf/bpftool/releases/tag/v7.8.1
0
2
0